Botveil Checkout Protection For WooCommerce Wordpress Plugin - Rating, Reviews, Demo & Download

Plugin Description
Botveil scores every checkout attempt, on the classic shortcode checkout and the Checkout block, and decides what to do:
- Allow – normal orders go straight through.
- Require email code – risky orders must enter a 6-digit code sent to the billing email.
- Hold for review – the order is placed but put on hold.
- Block – the checkout is refused with a generic message.
How the score works
Signals add points: guest checkout, many checkout attempts from one IP, failed payments (card testing), wrong or excessive verification codes, high order value. Trusted returning customers subtract points. You choose the thresholds and the action for low, medium and high risk.
Limits and bans
- Rate limits per IP and per email, with an inline “N attempts per X seconds / minutes / hours” setting.
- Too many checkout attempts from an IP, or too many wrong codes for an email, blocks and bans that IP or email for a while. Repeat offences get longer bans (15 min 1 h 4 h for IPs by default). Email bans never affect a customer logged in with that email.
- The dashboard lists active and recent bans with the IP or email, the matching customer, a link to their events, and Unblock.
Verification popup
The code popup copies your checkout’s fonts, colours, inputs and Place order button, so it looks like part of your theme. Every element can be restyled (typography, colours, spacing, borders, hover states, separate mobile values), with theme, system or Google Fonts. The code email uses your WooCommerce email design and is editable under WooCommerce Settings Emails.
Privacy by design
Emails and IP addresses are stored only as keyed hashes (HMAC-SHA256) for scoring and the event log. Only an active ban keeps the banned IP or email, encrypted, so staff can identify and lift it; it is deleted with the ban. Personal data export and erasure are supported, and the plugin suggests privacy policy text.
Monitor mode
Start in monitor mode to see what would be challenged or blocked without affecting customers, then switch to enforce.
External services
This plugin connects to Google Fonts only if an administrator picks a Google Font in Settings Botveil Popup design.
- What and when: when the popup design is saved, the site downloads the stylesheet for the chosen families from
https://fonts.googleapis.comand the font files fromhttps://fonts.gstatic.com, and stores them inwp-content/uploads/cshield-fonts/. Shoppers’ browsers then load the fonts from your own site and never contact Google. - Data sent: the font family names and weights, plus the request metadata any HTTP request carries (your server’s IP address and a user agent). No visitor, customer or order data is sent.
- Provider: Google LLC — Terms of Service, Privacy Policy, Google Fonts FAQ.
No other external service is used. Verification emails are sent through your site’s own mailer (WooCommerce / wp_mail).
Screenshots
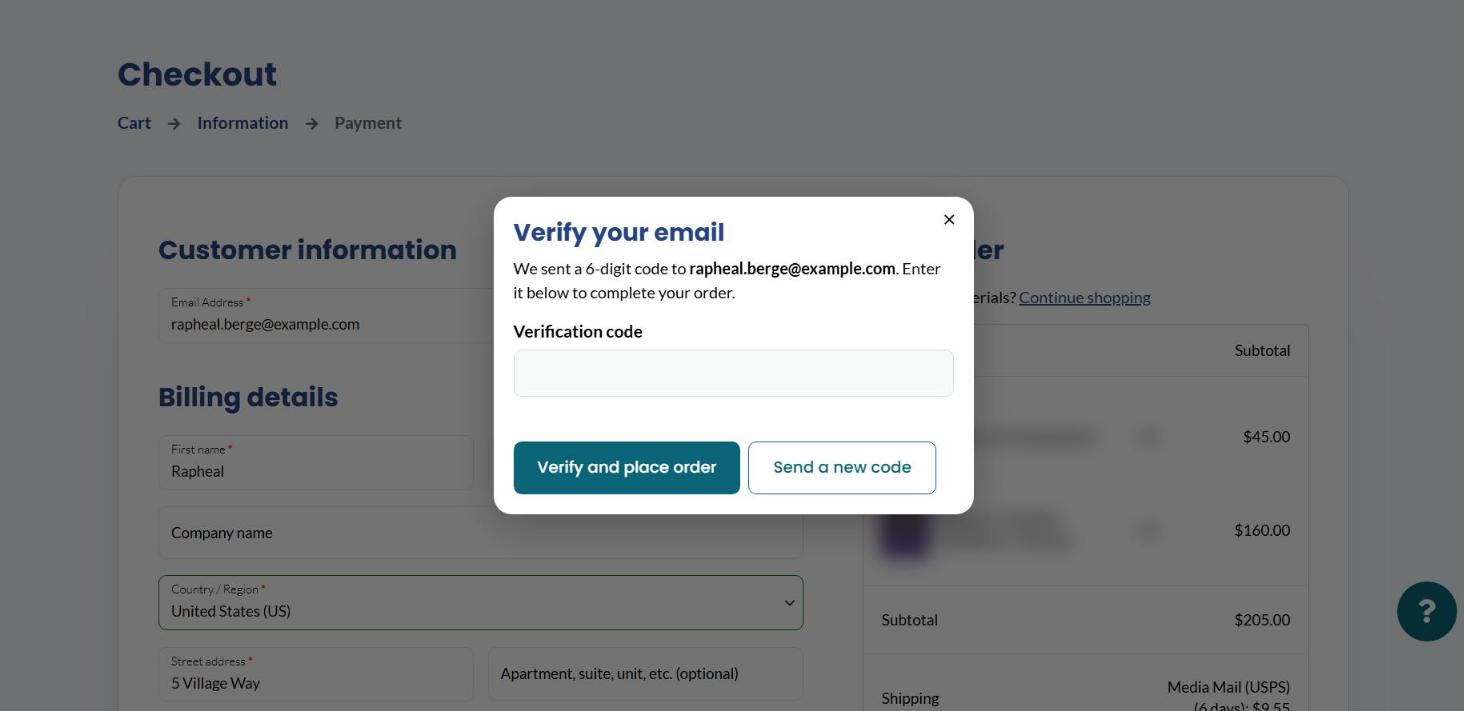
A risky checkout asks the shopper for a 6-digit code sent to their email. The popup copies the checkout’s fonts, colours and buttons.
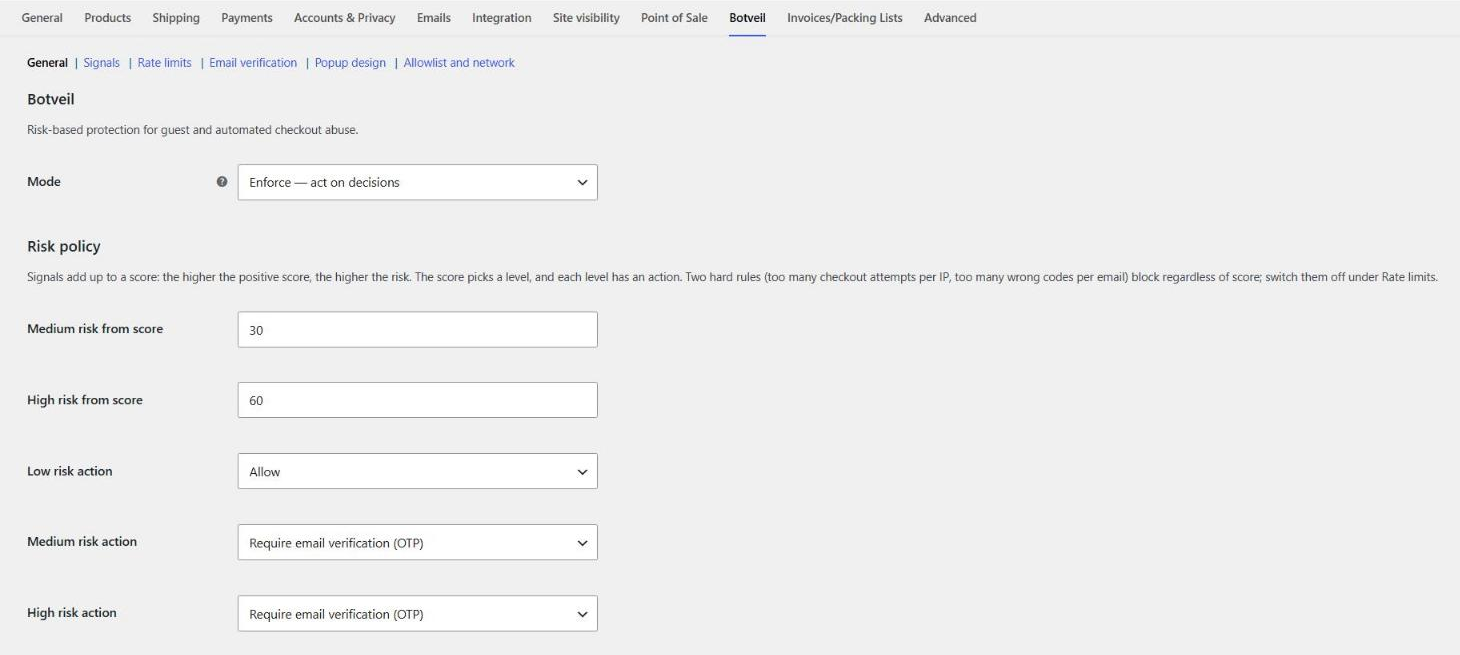
Settings → Botveil → General: choose the mode, the risk thresholds and the action for each risk level.
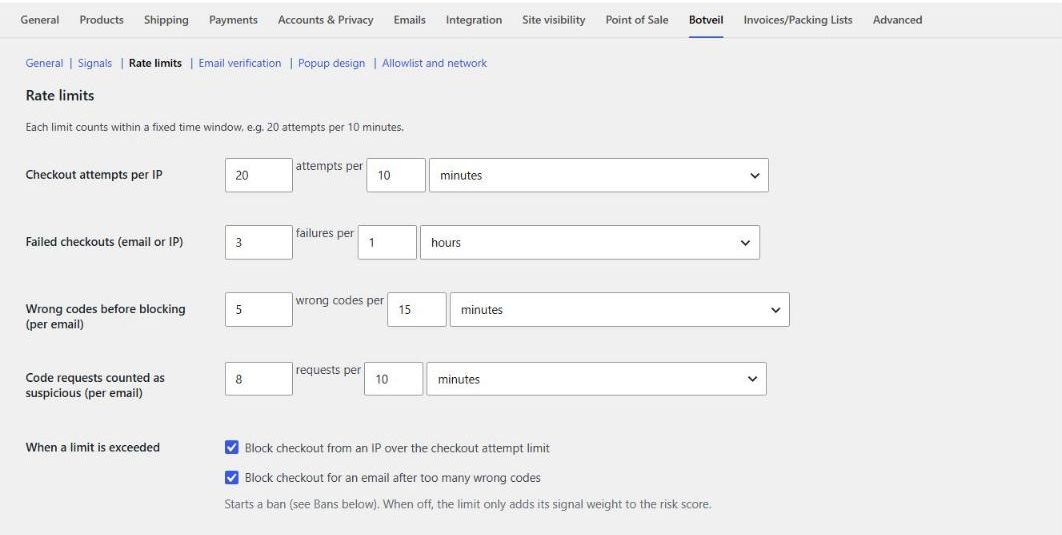
Rate limits per IP and per email, and what happens when a limit is exceeded.
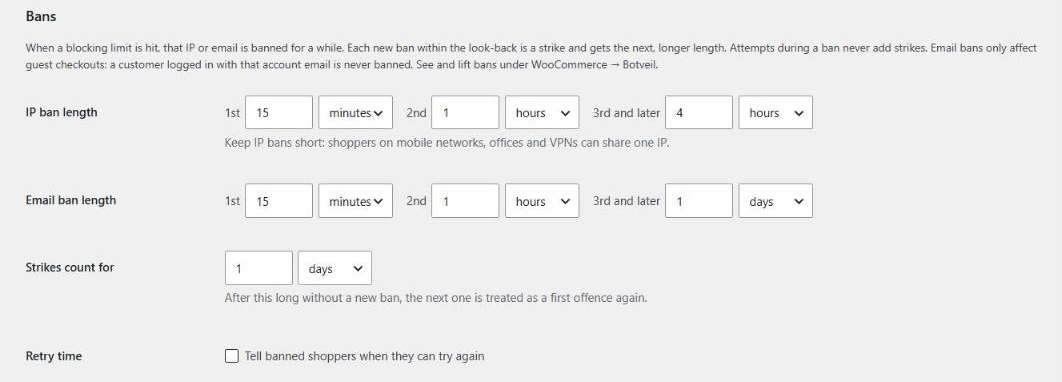
Timed bans that get longer for repeat offenders.
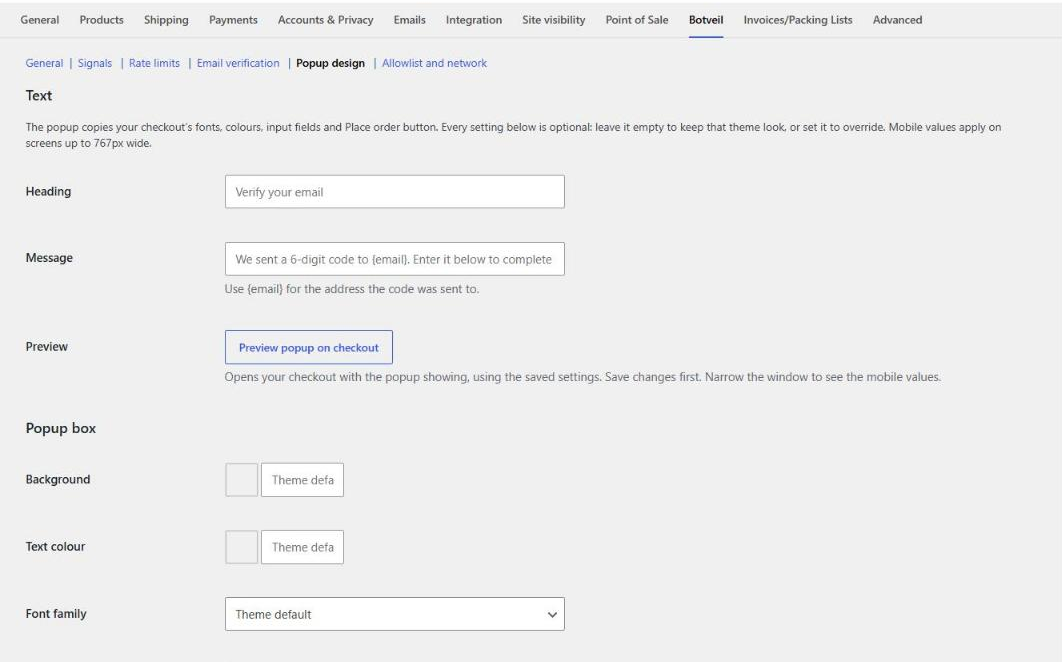
Popup design: restyle every part of the verification popup, with separate mobile values.
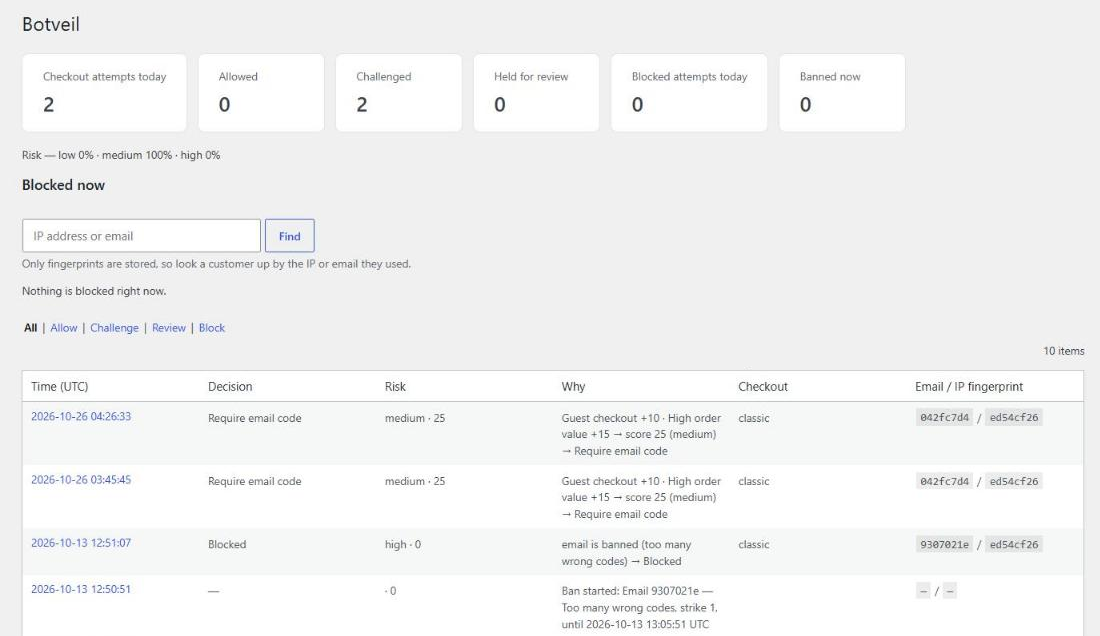
The Botveil dashboard: today’s activity, current bans and the event log with the reason for every decision.

Event detail: the signals that fired and their points.