Ropeline Wordpress Plugin - Rating, Reviews, Demo & Download
Plugin Description
Bots try to break into WordPress sites all day, mostly at the login. Ropeline stands at the door.
Login. Bots guess passwords thousands of times a day. Ropeline locks out an address after 5 wrong passwords in 15 minutes. Each lockout in the same day lasts longer: 15 minutes, then an hour, then a day. It covers wp-login.php, the WooCommerce My Account login, XML-RPC (including system.multicall, where one request can try hundreds of passwords) and application passwords.
Botnets spread their guesses over thousands of addresses to stay under limits like that, so Ropeline also watches each account. When one account fails 10 times in an hour from 3 or more addresses, it only opens on devices that have logged in before, for an hour. The real owner can always get in by resetting their password by email.
Password reset emails are limited too, so bots cannot flood anyone’s inbox.
Prove you’re human (optional). If a limit ever stops a real person, for example because a bot on the same Wi-Fi caused a lockout, they can pass a quick Cloudflare Turnstile check and carry on at once. Add your free Turnstile keys in Settings to switch it on.
Learning mode. For the first 7 days Ropeline only watches and records what it would have stopped, so you can check it will not get in anyone’s way. Then it starts blocking.
Plain English. The Overview shows every failed login and lockout with its address, an “Always let in” button and a one-click Unlock box. A Dashboard widget sums up the week.
Free, with no limits. Everything above is in this plugin, free, with no trial and no account. It never contacts Ropeline.
Ropeline Pro (optional, paid). A separate add-on from getropeline.com, with a 14-day free trial: leaked-password checks, hidden usernames, card-testing protection for WooCommerce checkout, fake-signup and spam blocking for comments, reviews and contact forms, verified AI-shopper checks, card-skimmer alerts, a weekly report and the Ropeline Network, where sites warn each other about the bots they stop. This plugin works fully without it.
External services
Ropeline connects to one outside service, and only if you switch it on. It never contacts Ropeline itself.
Cloudflare Turnstile (challenges.cloudflare.com), only if you add Turnstile keys in Settings, and only when a visitor stopped by a limit opens the “prove you’re human” page. That page loads Cloudflare’s Turnstile script in the visitor’s browser, and your site sends the one-time token and your secret key to Cloudflare to confirm it. Terms, Turnstile privacy addendum.
Privacy
Ropeline keeps a log of what it stopped and watched, with the visitor’s IP address and, for failed logins, the username tried. The log is deleted after 30 days. Lockout counters expire within a day. When someone logs in, Ropeline sets a cookie (ropeline_device_ followed by the user’s ID) that marks the browser as one they use, so it still works if their account is ever under attack; it holds a timestamp and a signature, nothing else, and lasts a year. Someone who passes the optional “prove you’re human” check gets a ropeline_human cookie with a timestamp and a signature that lasts an hour. Nothing is sent to Ropeline.
Screenshots
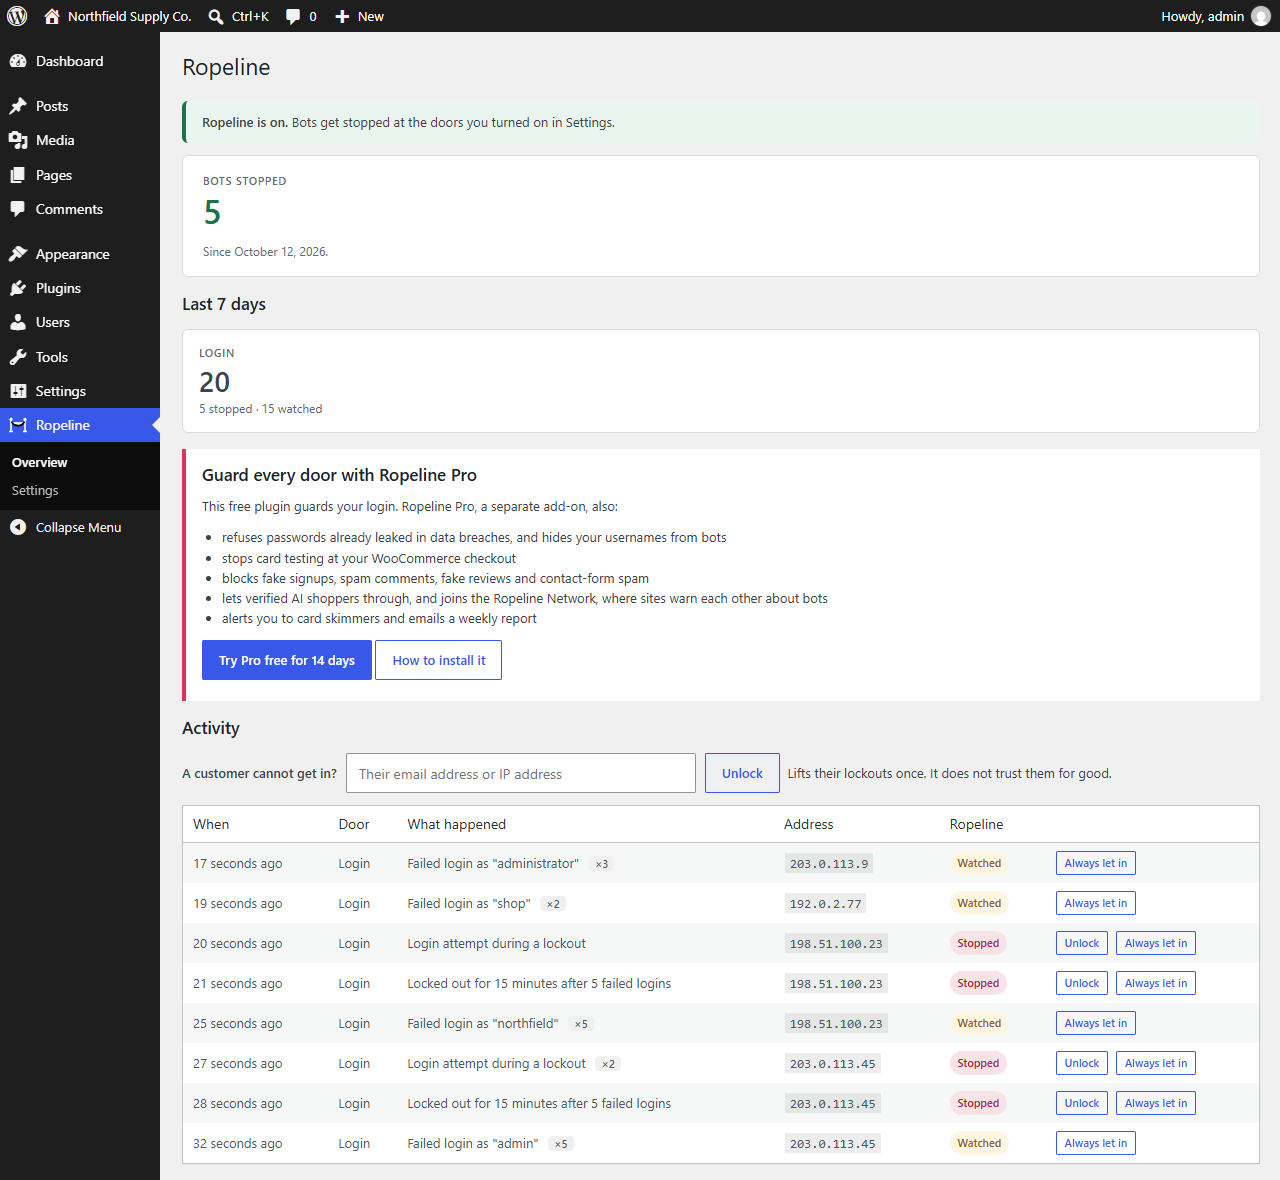
The Overview: bots stopped, and every failed login and lockout in plain English, with an “Always let in” button.
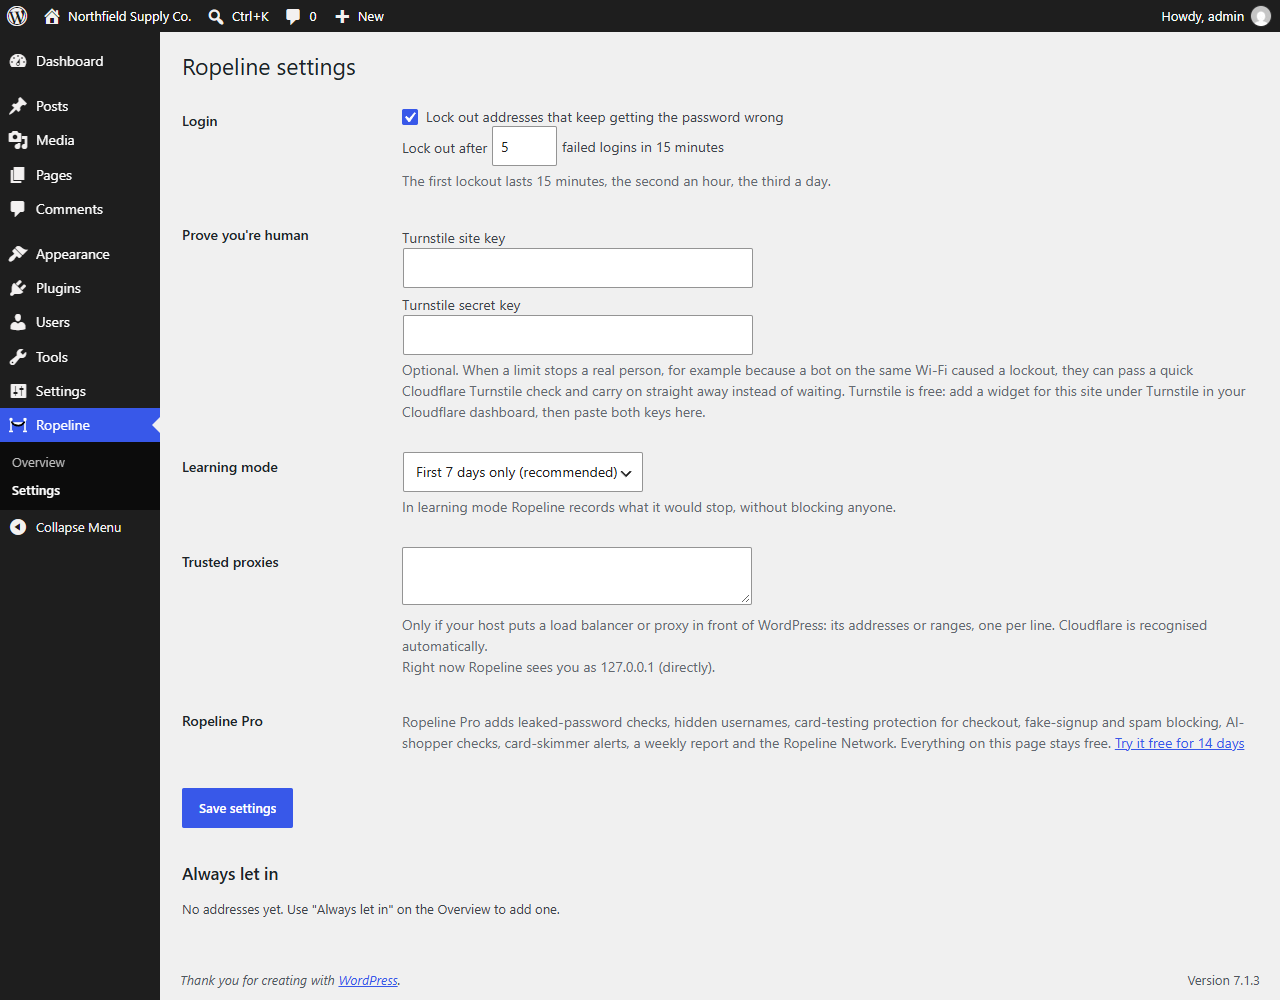
Settings: login protection and learning mode, with safe defaults.