Gracewell Security Suite Wordpress Plugin - Rating, Reviews, Demo & Download
Plugin Description
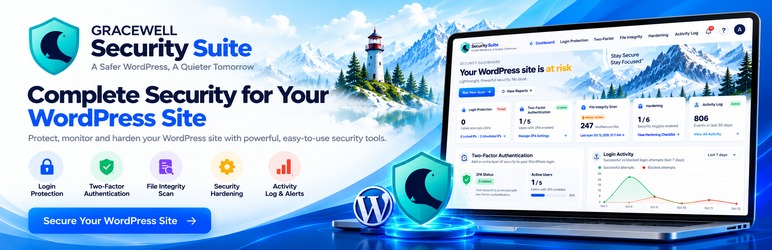
Gracewell Security Suite provides these security tools:
- Login attempt limits, IP lockouts, IP/CIDR allowlisting and an optional custom login URL.
- TOTP authentication compatible with Google Authenticator, Microsoft Authenticator, Authy and other standard authenticator apps. Enrollment requires verification. Secrets are encrypted, backup codes are hashed and single-use, and trusted devices can be revoked.
- Per-user 2FA, optional enrollment for other roles, administrator requirements and individual user setup requirements. Required users must complete setup before normal access resumes.
- Manual WordPress core checksum verification, modified/missing core file reports, suspicious uploads and backdoor-pattern detection in plugin/theme PHP files. Core findings support bounded text differences and checksum-verified restoration. Suspicious files can be quarantined.
- Hardening controls for XML-RPC, the file editor, version disclosure, user enumeration, security headers and executable scripts in uploads. Risk and passed/failed checks are calculated from enabled protections.
- Activity logging, configurable retention, exports and responsive light/dark admin themes.
The scanner uses official WordPress.org core checksums. Plugin and theme checks are signature checks rather than official package integrity verification. Scan scope is bounded on large sites. Suspicious findings require review; they are not proof of malware. No external authentication service receives TOTP secrets.
Uploads execution protection writes Apache 2.4 .htaccess rules. Nginx and other servers require equivalent server configuration. Security headers should be tested with your site’s integrations.
Settings and privacy
Global preferences save to the WordPress database. Automatic updates follow standard WordPress plugin update controls; host policies can still manage updates. Language follows the WordPress locale with English fallback: no translations are bundled. Log timestamps follow the WordPress site timezone and cron uses UTC. These controls do not change site settings.
No telemetry service exists in 1.0.0 and telemetry is disabled. Debug logging emits only a fixed settings-failure diagnostic to the server PHP error log when opted in; it never logs request payloads. Proxy detection requires an explicit array of trusted immediate proxy IPs in GWQSH_TRUSTED_PROXIES. X-Forwarded-For is walked from the trusted end to the first untrusted hop. HTTPS redirects are limited to suite pages on sites already configured for HTTPS; configure core HTTPS detection correctly behind TLS-terminating proxies.
When enabled, critical issue notices appear in a Security alerts panel below the suite page header, with links to the relevant settings or File Integrity page. Other WordPress admin screens use standard admin notices. Saving global settings updates the panel immediately. Enabling HTTPS enforcement on an HTTP site shows configuration guidance until WordPress HTTPS is configured.
Plugin status controls login protection and hardening. Existing enrolled 2FA remains enforced to protect accounts. Deactivation preserves enrollment. Import/export and reset cover global preferences only, never security credentials. Legacy authorization grants are invalidated on upgrade and require fresh factor verification.